
Switch 2 modding report details ns2jb exploit and its current limits
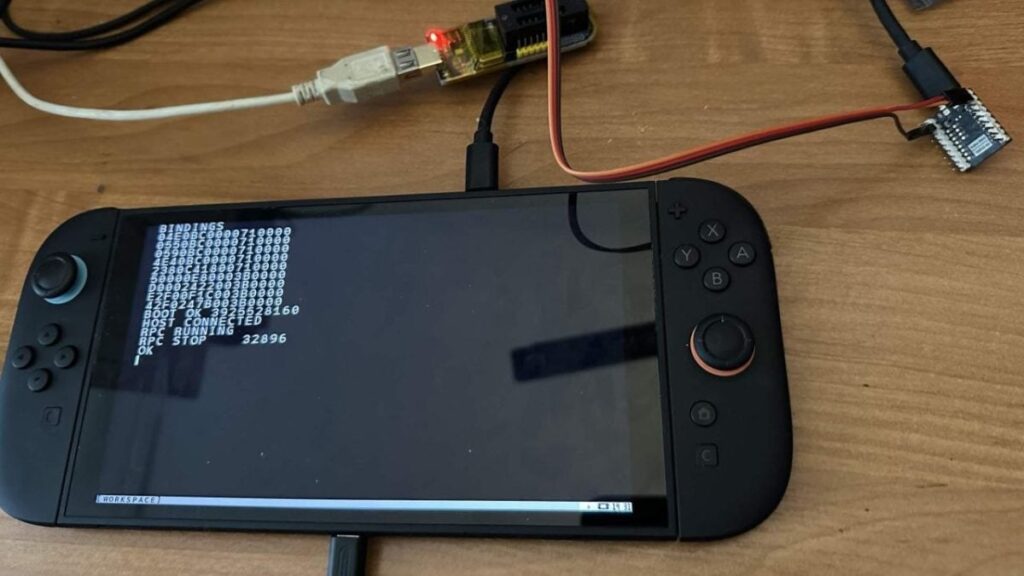
A reported Switch 2 exploit called ns2jb could give homebrew developers and game researchers another route into Nintendo’s console, although its claimed capabilities stop short of custom firmware. In a November 1 report, GBAtemp attributes the technical release to developer pepsipu and describes a software-only, tethered exploit.
The report says ns2jb supports firmware 23.0.1, but qualifies the broader jailbreak claim with uncertainty about its credibility. Its account should therefore be read as reported capabilities rather than independent confirmation that every Switch 2 owner can reproduce the results.
What the exploit reportedly reaches
According to GBAtemp’s summary of the technical write-up, the entry point is a 32-bit integer overflow in the backward-compatible Switch 1 SmileBASIC interpreter. The reported result is arbitrary native code execution inside the console’s filesystem and ro system modules.
GBAtemp lists potential uses including dumping encrypted Switch 2 save files, reverse engineering exclusive games and accessing hardware through memory-mapped input/output. It also describes a demonstration video showing modified characters in Mario Kart World. Those claims concern access and experimentation; they do not establish a finished homebrew platform or emulator.
Rebooting removes the payload
The limitations are substantial. GBAtemp says full kernel control remains unavailable, there is no custom firmware, and the exploit does not persist through a restart. Rebooting reportedly restores the original system processes and clears the payload from memory.
For Switch 2 modding, the distinction between temporary code execution and persistent system control matters: the reported access could support research without delivering the broader functionality users may associate with a complete jailbreak. GBAtemp also mentions reports of bricked consoles, while explicitly saying it could not confirm them. That leaves both reproducibility and practical safety unresolved in the supplied account.