Switch 2 modding reaches filesystem access, but ns2jb still has clear limits
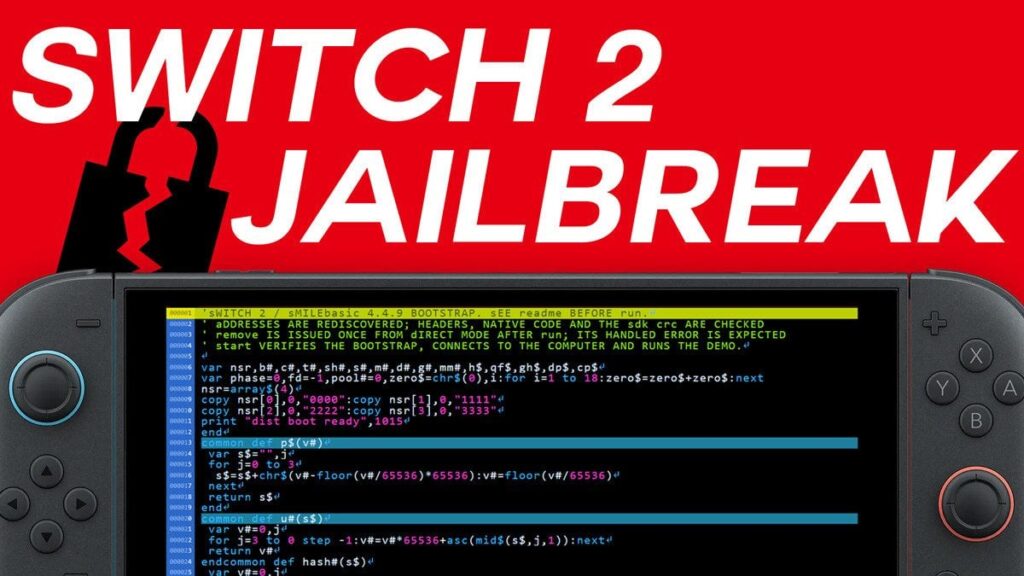
Switch 2 modding has a demonstrated foothold, although the available exploit falls short of a complete console unlock. According to GBAtemp’s October 28 report, security researcher Sammy “pepsipu” Hajhamid’s ns2jb allows native code execution with the privileges of the console’s filesystem service on firmware 23.0.1.
The researcher announced the work on October 22, sharing footage of custom character models in Mario Kart World. GBAtemp also reports that pepsipu used the access to extract internal storage and ordinary system-module code for offline analysis.
What the jailbreak currently enables
As described by GBAtemp, ns2jb is a software-only exploit that loses its effect when the console restarts. It does not provide custom firmware or a kernel compromise. Those boundaries matter: demonstrated game modifications do not establish that the console can install or launch backed-up games.
The documented route begins in SmileBASIC 4, a Switch title with programming tools, before exploiting the filesystem service and the system loader’s trust in that service. GBAtemp reports that Nintendo subsequently removed SmileBASIC 4 from the eShop.
Homebrew development has also produced a launcher that executes code through SmileBASIC’s GPU shaders, according to the report. That is a distinct capability from launching an independent native application.
Broader claims remain unproven
GBAtemp attributes to researcher hexkyz the assessment that filesystem access could theoretically support broader binary dumping. However, the report says no full game dump has been demonstrated, and claims surrounding specific Switch 2 dumps remain disputed or unverified.
Persistence across reboots and alternative entry points are possibilities discussed by researchers, rather than established features. For anyone following Switch 2 homebrew, the practical distinction is between the access already demonstrated and the wider capabilities developers still hope to achieve.